

On 7 September 2026, a senior cloud researcher at the National Cyber Security Centre published a short post on shadow AI: four headings, three named risks, two recommendations.1 One sentence in it is the most useful thing a British public body has published about enterprise AI adoption this year.
“Where cyber security policies cannot meet business needs, organisations are likely to continue seeing their employees adopt new AI services before they have had time to assess them and provide approved alternatives.”
That is the diagnosis, and it is correct. It is also the last line of the section it appears in. The next thing on the page is a heading reading What are the cyber security risks of shadow AI, and the cause is never returned to.
A declaration first, because this argument finishes somewhere convenient for me. Arkava, the company I founded, sells agentic automation to organisations that want measurable outcomes faster than their current delivery can produce them. An article arguing that shadow AI is evidence your organisation is too slow ends, followed far enough, at engage somebody who can — which is worth knowing before you weigh anything below it. Nearly all of the evidence that follows is the NCSC’s own published work rather than mine.
The diagnosis is right. Framing it only as risk is what does the damage
Here is the argument I want to make, labelled as mine. The problem with that blog is not what it says. It is the proportion.
Shadow AI is presented as a risk surface and almost nothing else. Three headings of exposure — data leaving the organisation, loss of visibility and control, agents as a new attack path — and one clause at the end of the penultimate bullet, conceding that understanding why people do it helps organisations “support innovation safely”.1 The cause gets a sentence. The consequences get the page.
That proportion is not neutral, because of who reads it. Frame a subject wholly in the vocabulary of exposure and you trigger the trained reflex of the profession receiving it. Cyber security people are selected, promoted, and audited on preventing bad outcomes, and a document describing only bad outcomes produces the behaviour that prevents them: longer assessment cycles, more committee stages, more deliberation before anyone may try anything. Governance that restricts rather than enables. Governance that deliberates rather than distributes.
Which is precisely the condition the NCSC’s own sentence identifies as the cause. Policies that cannot meet business needs produce shadow AI; a risk-only framing produces slower policy; slower policy produces more shadow AI. The advice, read by its intended audience in the way that audience is trained to read it, reinforces the thing it is trying to reduce — and nobody in that loop is doing anything unreasonable at any step.
Then there is the line addressed to employees: “Encourage staff to choose wisely.”
An employee can only choose wisely between things they have been given, and only judge wisely if somebody has explained what makes one option worse than another. Neither is in their gift. This is slopey shoulders from a profession more fluent in the vocabulary of accountability, risk ownership, and duty of care than almost any other function in a business — it will spend an afternoon arguing whether a risk is owned by the CIO or the COO, then hand the residual to a marketing executive with a deadline. If the duty sits anywhere, it sits with whoever decided not to provide the approved alternative.
The only number in it belongs to the company selling the remedy
The blog carries one statistic: “Recent research suggests that using shadow AI is widespread, with one study finding that nearly three-quarters of employees (71%) reported using AI tools that have not been approved by their employer.”1
Follow the link on the words one study. It goes to a Microsoft marketing page, published 13 October 2025, reporting a Censuswide poll of 2,003 UK employees that Microsoft commissioned, on a page arguing that organisations should adopt Microsoft 365 Copilot.2 Eleven-month-old vendor communications, described by the national technical authority in September 2026 as recent research, supporting a conclusion that happens to be the sponsor’s product strategy. The NCSC also rounds 71 per cent up to “nearly three-quarters” and leaves behind the better figure on the same page: 51 per cent still doing it every week.2 Ever-used is a headline. Weekly use is a governance fact — it is the number that tells you a workflow has formed.
There is better UK evidence, and it is free. In June 2026 the Office for National Statistics found around 35 per cent of UK businesses with ten or more employees using at least one AI technology, from 38,637 responding businesses, and only 10 per cent of those adopters describing the use as extensive.3 The same month, the ONS found 55 per cent of employees in Great Britain using AI for work or education.4 Two surveys, two populations, two questions, as the ONS says itself — the gap does not tell you a fifth of the workforce is operating covertly; it tells you the organisational picture and the individual picture were never reconciled. Say that caveat out loud. A number that survives being explained is worth more than one that does not.
All of this was published in 2023, about a different noun
On 27 July 2023 the NCSC published guidance on shadow IT. It was last reviewed on 14 August 2026, three weeks before the shadow AI post. It says this:5
“Shadow IT is rarely the result of malicious intent. It’s normally due to employees struggling to use sanctioned tools or processes to complete a specific task.”
Its list of causes is a list of unmet needs, named as such: not enough storage, no way to share data with a third party, no access to services such as development tools, no sanctioned video conferencing or instant messaging, and an asset-request process that is ineffective or slow.5 Every item is a delivery failure described from the employee’s side of the desk.
Then, on 4 June 2025, the NCSC published its cyber security culture principles. The first of the six reads: “Frame cyber security as an enabler, supporting the organisation to achieve its goals.” The fifth reads: “Leaders take responsibility for the impact they have on security culture.”6
So the UK’s national technical authority has published, across three years, that people bypass controls because the sanctioned route does not work, that security should be framed as an enabler, and that leaders own the consequences of how they frame it. The September 2026 post links to both of those documents — the doctrine is not missing; the newest document is simply the one departing from it.
That is the whole of my “no different from shadow IT” claim, and it needs its limit stated, because a CISO will raise it within ten seconds and be right to. The cause is identical and the governance answer is identical. The blast radius is not. A spreadsheet copied into an unapproved file-sharing account sits somewhere you did not choose. The same spreadsheet pasted into a consumer AI service may be retained and used to improve that service, cannot be retrieved, and — at the agentic end, where the tool is handed access rather than content — does not merely hold your data but acts with it.7 Same cause, same remedy, larger consequences; the middle term is the one organisations keep skipping.
You cannot manage what you do not know. You also cannot claim to be surprised by what you were told in 2023.
The signal is data. It is not a shopping list
Shadow AI is an indicator, and indicators are not free. Somebody found a task that mattered enough to solve without budget, without permission, and without asking, and then did it repeatedly. That is a completed, user-validated experiment, and your organisation paid nothing for it except the risk it did not price.
Every unapproved tool in your organisation is a business case somebody already wrote, tested, and adopted without asking you for a penny of budget.
Ian Malcolm’s line about life finding a way is usually quoted as though it were about dinosaurs. It is about the designers, who built a park on the assumption that controlling a thing and understanding it are the same activity, and who could therefore only ever be surprised by their own system. Demand for capability behaves the same way. It does not care about your approval process, it routes around obstruction by default, and the fences will tell you it got out without ever telling you why it wanted to leave.
This is where I part company with a position close to my own. On this show in August, Sam Parkinson of Mettle Studio placed shadow AI at rung two of a five-rung maturity ladder — the company bought nothing, approved nothing, and secured nothing, and everybody is using it anyway — and argued that most organisations should buy the licence and let the appetite that surfaces tell them what to build.8 I said then that I would not, and I still would not. Reading the signal is not the same as buying whatever produced it; the tool your people reached for is rarely the right long-term answer, only the nearest available one. What the signal reliably tells you is that a gap exists, that it matters enough for somebody to take a personal risk over it, and that something in the market already addresses it. Worth a great deal. Not a procurement decision.
Reading this far?
Subscribe to The Control Layer for one piece a week in this register — AI, cybersecurity, sovereignty, and the geopolitics of the technology stack. Free.
How to tell a demand signal from a corner being cut
Not all of it is a signal. Some of it is somebody doing less work than they were paid to do, and a leader who treats every instance as suppressed innovation is going to launder some laziness. Two tests, applied case by case, separate them.
The purpose test. Did it make a measurable difference to an activity that directly serves what the organisation exists to do? Not did it feel faster. Did the work change. If the answer is no measurable difference to meaningful work, you are looking at a shortcut, and it should be handled as one.
The controls test. Does it breach a control you hold for a regulatory, contractual, or due-diligence reason — and can you name which one, without reaching for a policy document written to cover everything? A control you can name is a boundary. A control you cannot name is a habit.
A use that passes both is a capability gap you should be funding. A use that passes the purpose test and fails the controls test is the most valuable case of all — the demand is real and the blocker is now named, which means you know both what to build and what it has to satisfy. A use that fails the purpose test is a management conversation, and not an AI problem.
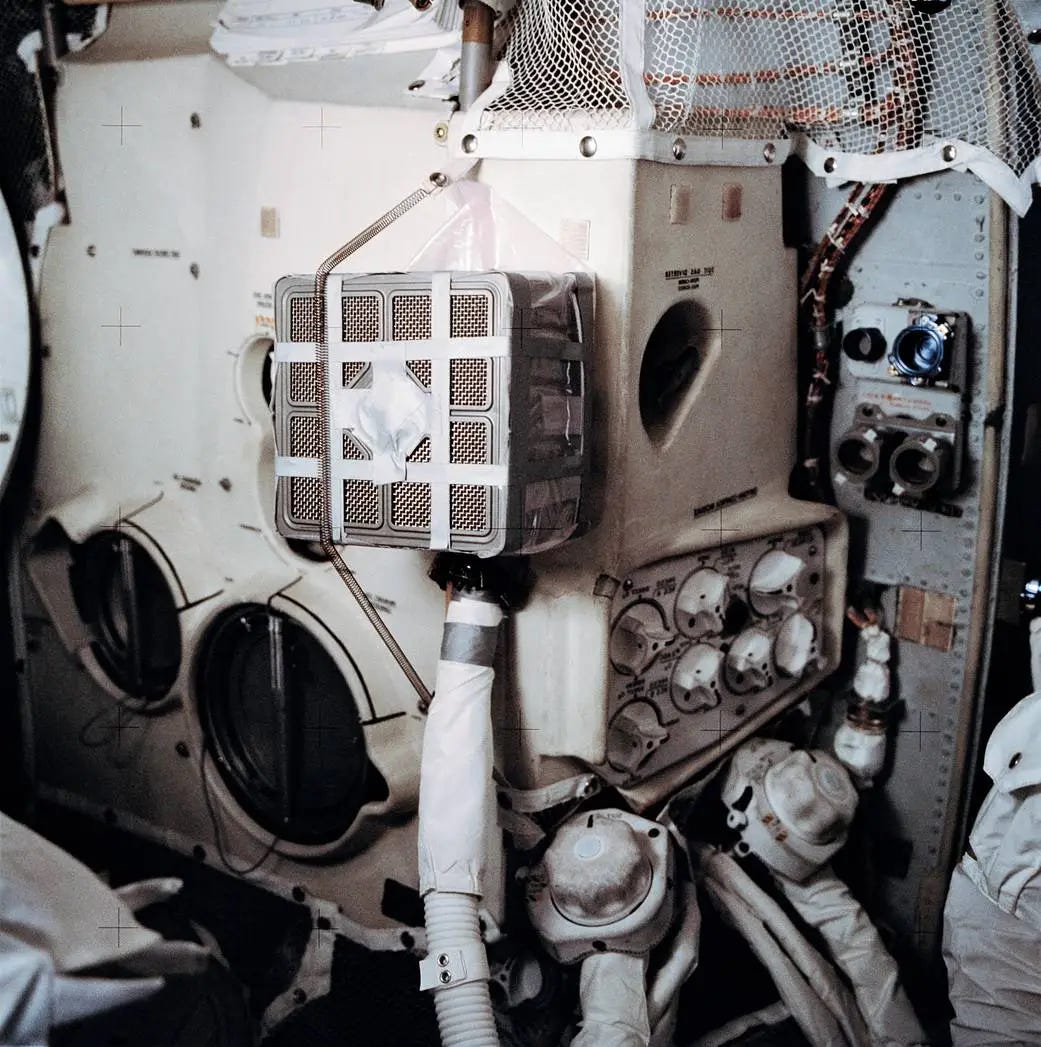
When Apollo 13’s carbon dioxide scrubbers failed, the response on the ground was not an inquiry into unauthorised deviation from the flight plan. It was a table, everything the crew physically had on board, and an instruction to work the problem. Nobody asked whether the crew had improvised. They asked whether it would hold — the purpose test, run under the only deadline that has ever concentrated an engineering team properly.
I have been the blocker in this story
Before founding Arkava I spent six years at a large construction and development group, latterly as director of IT and of cyber security and compliance, and before that as a senior digital business partner. That last role existed because of this exact problem.
Global IT policy sat on one side. On the other sat project teams fighting for every inch of margin and programme, who would find, buy, and stand up a solution the moment the sanctioned route took longer than the problem could wait. Some of what they built was genuinely good and nobody in the centre knew it existed. Some of it was poorly conceived, expensive to keep alive, and became somebody’s problem years later — both outcomes from the same root, and the root was never the project teams.
My job was to challenge both sides in equal measure. With the business: here is the risk you are actually carrying, and here is why the practice exists. With IT: here is why they need it, what it is worth, and the specific blocker you are going to remove so this stops happening behind you. Nobody was acting in bad faith. The organisation had simply built a structure in which the fastest route to doing your job well ran outside the structure.
I was the mediator on a good day. On the days I lost the argument in the centre, I was the blocker.
Predictive judgement
By 31 December 2027, at least one UK organisation will publicly attribute a reportable data incident to an employee’s use of an unapproved AI service, and the account will state that the approved alternative either did not exist or was inadequate for the task.
Signals to watch. The Information Commissioner’s Office enforcement and reprimand register; Financial Conduct Authority supervisory and final notices; and the wording of first-party breach disclosures — whether the cause is described as employee misconduct or as a need the organisation failed to meet.
What would falsify it. If neither the ICO’s enforcement and reprimand listings nor the FCA’s supervisory publications carry such an attribution by that date, the prediction fails and I will say so here. I name those two registers deliberately: “nobody disclosed it” is not evidence of anything, and a prediction that can pass on silence is not a prediction.
I expect the admission rather than merely the incident for institutional reasons. Asimov’s Seldon Crises work because the disruption is legible in the data long before the Empire will concede it, and the Empire’s move is never denial — it is reclassification, filing the problem under a heading it already knows how to process. Shadow AI is currently filed under employee behaviour. The first organisation to refile it as delivery failure will do so because a regulator made the other filing untenable.
The publication that calls its predictions in writing.
Every Control Layer piece ends with a falsifiable prediction and a list of signals to watch. Subscribe to track them. One email a week. Free.
The bottom line
The NCSC is right, it was right in 2023, and its own first principle of security culture says to frame this as an enabler. The document that could not quite bring itself to do that is the one published three weeks ago.
If 71 per cent is anywhere near correct — and it is a vendor’s number, so treat it as a direction of travel — then most of your workforce has already run an experiment you did not authorise, did not fund, and cannot see. The useful question is not how they got round you. It is what they were trying to do, why the approved route could not, and how long you have known.
Shadow AI is not your staff going around you. It is your staff going ahead of you.
Go and ask three people in your organisation what they used an AI tool for last week. Not which tool. What for.
References
Amer Altaf is founder and chief executive of Arkava and managing editor of The Control Layer. Views expressed by guests are their own.
The Control Layer publishes weekly. Subscribe free.
Decision-grade analysis on AI, cybersecurity, technology sovereignty, and the geopolitics of the technology stack — written for the board paper, not the timeline. By Amer Altaf, Founder & CEO of Arkava and Managing Editor of The Control Layer.
One email a week. No paywalls on the analytical pieces. Unsubscribe in one click.
National Cyber Security Centre, The hidden risks of shadow AI, Simon B, Senior Cloud Researcher, 7 September 2026. https://www.ncsc.gov.uk/blogs/the-hidden-risks-of-shadow-ai ↩ ↩2 ↩3
Microsoft UK Stories, Rise in shadow AI tools raising security concerns for UK, 13 October 2025. https://ukstories.microsoft.com/features/rise-in-shadow-ai-tools-raising-security-concerns-for-uk/ — the survey is a Censuswide poll of 2,003 UK employees aged 18+, fieldwork October 2025, commissioned by Microsoft. Cited here as a vendor-commissioned figure, which is what it is. The NCSC blog’s “one study” link resolves to this page. ↩ ↩2
Office for National Statistics, Artificial intelligence in UK businesses: 2023 to 2026, published 20 July 2026. Business Insights and Conditions Survey wave 159, fieldwork 15–28 June 2026, 38,637 responding businesses. https://www.ons.gov.uk/businessindustryandtrade/business/businessservices/articles/artificialintelligenceinukbusinesses/2023to2026 — note that widely circulated secondary coverage reports 29 per cent, which is a different business-size population; the 35 per cent figure applies to businesses with ten or more employees. ↩
Office for National Statistics, Opinions and Lifestyle Survey, June 2026, on AI use by employees in Great Britain for work or education. ↩
National Cyber Security Centre, Shadow IT, published 27 July 2023, last reviewed 14 August 2026. https://www.ncsc.gov.uk/guidance/shadow-it ↩ ↩2
National Cyber Security Centre, Cyber security culture principles, 4 June 2025. https://www.ncsc.gov.uk/collection/cyber-security-culture-principles — principle one, “Frame cyber security as an enabler, supporting the organisation to achieve its goals”; principle five, “Leaders take responsibility for the impact they have on security culture”. ↩
ASD’s ACSC, CISA, NSA, Canadian Centre for Cyber Security, NCSC-NZ, and NCSC-UK, Careful Adoption of Agentic AI Services, 30 April 2026. https://media.defense.gov/2026/Apr/30/2003922823/-1/-1/0/CAREFUL%20ADOPTION%20OF%20AGENTIC%20AI%20SERVICES_FINAL.PDF — the co-sealed guidance the NCSC blog directs readers to, on limiting agent privileges and gating high-impact actions. See also NCSC, Thinking carefully before adopting agentic AI, 15 May 2026. https://www.ncsc.gov.uk/blogs/thinking-carefully-before-adopting-agentic-ai ↩
Sam Parkinson, co-founder of Mettle Studio, in conversation, The Control Layer, published 26 August 2026. The five-rung ladder and the rung-two formulation are his. My disagreement at rung three is set out in The mess that bills you twice. https://thecontrollayer.arkava.ai/p/ai-maturity-five-layer-readiness-test ↩